
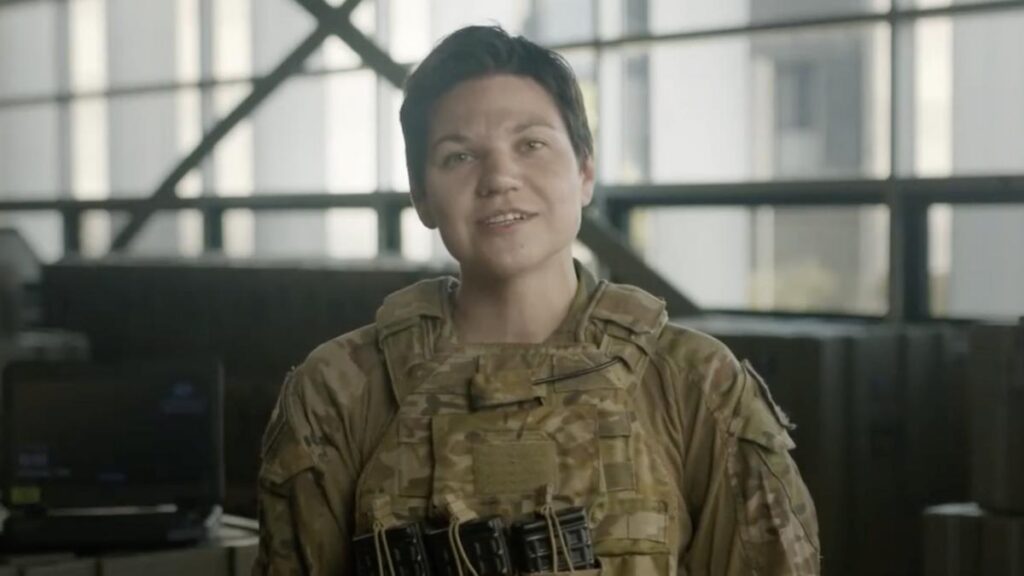
The criminal charges against former Australian Defence Force soldier Kira Korolev have been upgraded from “preparing for an espionage offence” to “conspiracy to commit espionage”.
The Australian Federal Police (AFP) announced the upgraded charge on 30 June 2026. The charge was decided by the Brisbane Magistrates Court on 29 June 2026. The new charge also applies to Korolev’s husband, Igor Korolev.
The Korolevs were originally arrested on 11 July 2024. Since then, the AFP and the Australian Security Intelligence Organisation (ASIO) have continued the investigation under the Counter Foreign Interference Taskforce led jointly by AFP and ASIO with other Commonwealth entities contributing. The two years of investigation has reportedly provided a more complete picture of the Korolev’s actions.
Crucially, it is alleged that there is now evidence of the Korolevs having entered into an ‘agreement’ with Russian authorities to provide sensitive ADF information. It is this alleged ‘agreement’ that has enabled prosecutors to argue the charge upwards in severity from preparation to conspiracy.
The upgraded charges also align with ASIO’s 2026 Annual Threat Assessment, which describes Australia’s security environment as increasingly “dynamic, diverse and degraded”, with espionage and foreign interference remaining at extreme levels. Rather than representing an isolated incident, the Korolev matter should be viewed within this broader national security context.
The charge “preparing for an espionage offence” is under section 91.12 of the Criminal Code Act 1995 (Cth) and the “conspiracy to commit espionage” under section 91.1(1). The latter charge requires proof of an agreement, which the AFP appears to have identified and the prosecution has argued exists.
This is the first instance of this specific charge of conspiracy being laid since the relevant 2018 national security law reforms were enacted. That 2018 legislation was created in response to Russian and Chinese interference activities both in Australia and overseas. The Act introduced offences of espionage (Division 91) and foreign interference (Division 92).
As Pentagram Advisory has noted in previous articles about the Korolev case, this is a textbook example of insider threat.
The Korolev case is so potent because Korolev was a member of the ADF which meant she would have been subject to rigorous background checking and security vetting to win employment in the ADF. Once in the ADF she would have been subject to ongoing security checking and education. There is a strong and mature security culture in the ADF and Defence more broadly.
Prima facie, the reported allegations that Korolev travelled to Russia without seeking permission from the ADF (she would have been obliged by ADF security practice to seek permission) and provided the log-in details for her ADF IT account to her husband, who was not authorised to access ADF information, seemingly demonstrate that Korolev chose to behave in ways that were not aligned with the security obligations that she would have accepted as part of her ADF employment.
Tech Times, in its 4 July 2026 report on this case, noted that there are features of the case that will be uncomfortable for Defence. Those features are as follows:
- Korolev’s IT account credentials were not suspended or restricted when she began long-term leave from the ADF in 2023. Reportedly there were account logins from December 2022 to July 2024 which could have signalled suspicious activity.
- Defence’s cyber security system apparently did not detect anomalous connection and usage between Korolev’s Brisbane home and Russia.
- The alleged transfer of ADF official information to a personal email address appears not to have triggered a Data Loss Prevention (DLP) response.
In the wake of the Korolev’s 2024 arrest, the Australian Strategic Policy Institute (ASPI) noted that ideological espionage cases seem (in 2024) to be trending upward globally. Preliminary research by ASPI’s Statecraft and Intelligence Centre suggests that ideology was a motivating factor in 35 of 79 espionage cases identified in Western countries since 2000, or 44 percent.
In August 2024, The Nightly reported that “Mrs Korolev [was] employed as an Australian Army information systems technician [and] has been secretly employed by Russian Basic Information Technologies, known as RusBITech, a high-tech corporation whose computer operating system Astra Linux powers the Russian armed forces.”
The Nightly reported further that “RusBITech is a contractor for the FSB, Russia’s domestic intelligence agency; FSTEC, its military information security agency; SVR, its foreign intelligence agency; and the Ministry of Defence, including military intelligence agency GRU.”
We do not know what the Korolevs’ motivations were. That should be uncovered through the court process, but whatever their motivation the damage, the consequence, can be the same.
This point is key to understanding the significance of the risk posed by insider threat.
Whether the insider causes harm unintentionally or intentionally, the consequences can be the same. In a standardised five-point risk scale the insider’s actions may cause insignificant to catastrophic harm with commensurate consequences for the entity they work for irrespective of intention.
For private sector entities there is another significant message. While this matter concerns Defence, the lessons extend well beyond government. Australia’s critical infrastructure operators increasingly hold information, systems and technologies of strategic interest to foreign intelligence services. The critical infrastructure entities, by definition, deliver products and services that are critical to Australia’s daily function, community wellbeing, and national security.
The ADF and Defence have a mature and active personnel vetting, cyber security, security education, security culture, and insider threat programs and yet have spawned in Korolev a significant insider threat case. Very few private sector entities, including critical infrastructure entities, will have security culture and processes near the level of the ADF. Accordingly, without these mitigations in place, these private sector and critical infrastructure entities face an elevated risk from the insider threat.
ASIO has also warned that some nation states are no longer simply collecting intelligence, but are preparing access that could enable future sabotage of Australian critical infrastructure. Insider threat and cyber security should therefore not be viewed as separate issues, but as complementary elements of organisational resilience.
What is the ‘take-away’ from this new development in the Korolev case? Insider threat is real, is not well understood, is increasingly relevant and probable in Australian workplaces, and can have grave consequences. The remedy is to understand the risk posed by insider threat and to begin to act to mitigate the risk.
Pentagram Advisory provides practical eLearning and advisory services to help organisations strengthen trusted workforce capability and manage insider risk, including the Trusted Workforce Program, the Pre-employment Screening and Workforce Assurance course, the Critical Worker Identification and Risk Management Framework course, the Foreign Interference: Understanding The Risk To Australia’s Critical Infrastructure course, and the Insider Threat Program course.